The short answer
If your WordPress site is hacked, take a full copy of the files and database first, then change your hosting, WordPress, database, FTP and email passwords from a clean device. Ask your host to take the site offline if visitors are being redirected. Clean it or restore a known-clean backup, then request a review in Search Console.
What to do in the first hour
Don't start deleting things that look wrong. That destroys the evidence of how the attacker got in, and a half cleaned site usually keeps a backdoor.
- Take a copy of everything as it is. Download the site files and export the database, or ask your host for a snapshot. Keep it apart from your good backups.
- Change passwords from a clean device. If the computer you normally use is infected, new passwords typed on it can be captured as well. Do hosting first, then WordPress admins, FTP, the database and email.
- Tell your host. They can check the rest of the account, and would rather hear it from you than suspend you after a spam complaint.
- Note what you saw and when. Times help when we read the server logs.
Signs your website has been hacked
Most hacks are built to stay out of the owner's sight. Signs to look for:
- Visitors who arrive from Google get redirected to a pharmacy, casino or scam page, while the site looks normal when you type the address in yourself.
- A site: search for your domain shows pages you never wrote, often in Japanese or stuffed with product names.
- Administrator accounts you don't recognise under Users.
- Posts or pages you didn't publish.
- PHP files inside wp-content/uploads, a folder that should only hold images and documents.
- A red warning page in Chrome before your site loads, or "This site may be hacked" under your listing in Google.
- An email from Google Search Console about security issues, or a suspension notice from your host for malware or outgoing spam.
- Your email suddenly landing in customers' junk folders.
Most hacked sites we see run WordPress, because so much of the web does, but these signs apply to any CMS.
What we found on one hacked WordPress site
One example, with identifying details left out. A training organisation's WordPress site had an administrator account that nobody in the business recognised. It wasn't a dormant leftover. It had live login sessions, so someone was signed in as that user, and roughly 200 spam posts had been published.
Two lessons from that site apply to most hacks. Deleting the spam posts achieves nothing while the account and its sessions exist, because whoever holds them can publish another 200 overnight. The account has to be removed and every session ended, which in WordPress means deleting the user and replacing the security keys and salts in wp-config.php so that existing login cookies stop working.
The second lesson: a rogue admin account is how an attacker keeps access, rarely how they got in. The original weakness, usually an outdated plugin or a reused password, still has to be found.
What a proper cleanup includes
A scanner plugin matches known patterns, and attackers rewrite their code to dodge them, so a clean scan proves little. Our cleanups cover:
- Server access and error logs reviewed for the entry point and the date it started.
- WordPress core replaced with a fresh copy of the same version from wordpress.org, rather than patched file by file.
- Every plugin and theme reinstalled from its official source. Pirated ("nulled") premium plugins are removed, as they are a common way malware arrives.
- The uploads and mu-plugins folders, every .htaccess file and wp-config.php checked by hand for injected code.
- The database searched for injected scripts in posts and options, unknown users and spam content.
- WordPress and hosting cron jobs checked, since malware often reinstalls itself from one.
- Other sites in the same hosting account checked, because one infected site can reinfect its neighbours.
- Passwords, keys and salts rotated, then everything updated.
- Spam URLs left returning a 404 or 410 so Google drops them, and the sitemap resubmitted.
Google warnings and asking for a review
Google picks up hacked sites through Safe Browsing and its normal crawling. Depending on what it finds, your listing may carry a "This site may be hacked" label, or Chrome and other browsers that use Safe Browsing may show a full page red warning before anyone reaches you.
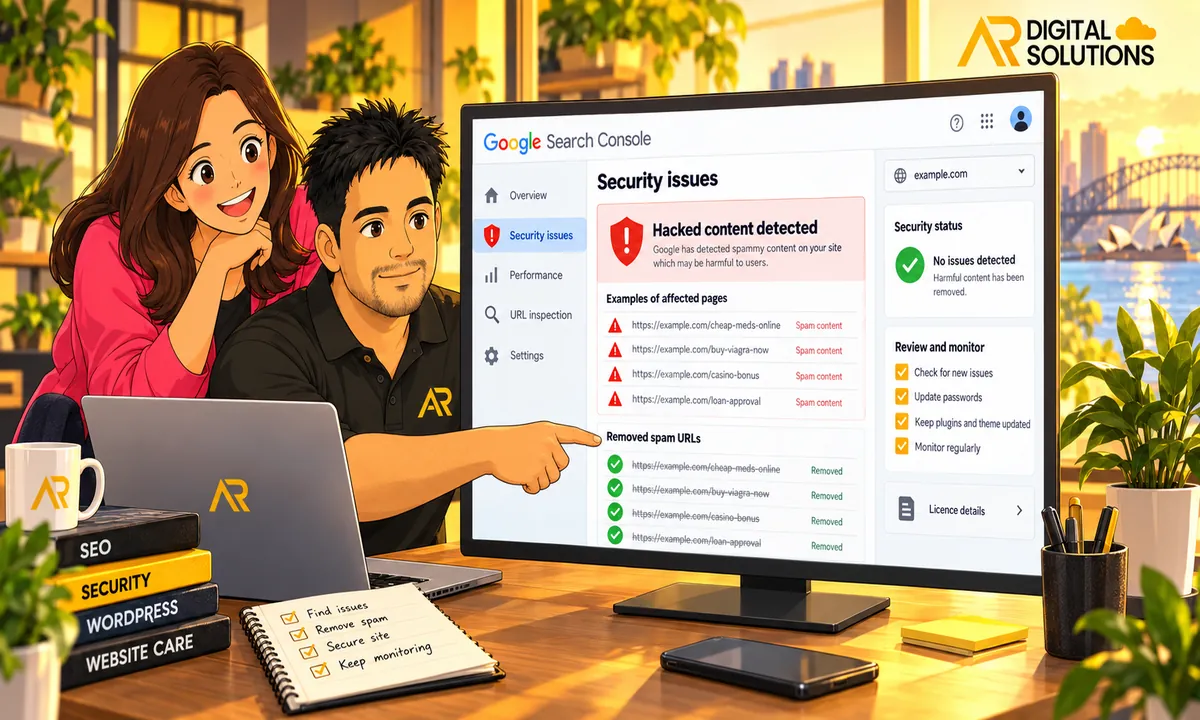
In Search Console, open Security issues under Security & Manual Actions. It lists the kind of problem Google detected, such as hacked content, malware or deceptive pages, usually with sample URLs. Read the samples: they show what Google saw, which can differ from what you see logged in.
When the site is genuinely clean, tick the box confirming you have fixed the issues and click Request review, with a plain description of what you did. Google's turnaround depends on the issue type and can run from about a day to several weeks. If problems remain the request is declined and you go back to the start, so finish the cleanup before you ask. The site must be verified in Search Console first.
Stopping it happening again
Reinfection usually comes from the same small set of causes, and the fixes are dull ones that work:
- Core, plugin and theme updates applied every week or two instead of once a year.
- Plugins you no longer use deleted rather than left deactivated.
- Two-factor login for every administrator, and fewer administrators. Editors don't need admin rights.
- File editing in the dashboard switched off (DISALLOW_FILE_EDIT in wp-config.php), so a stolen login can't rewrite theme files.
- Backups stored off the server and restored in a test now and then, so you know a clean point exists.
On sites we manage, our team applies updates and runs daily backups, and every site gets a firewall and login protection, as described on our WordPress website builds page. That ongoing work sits in our managed support care plans, which start from $249 a month for hosting, updates, security and small changes. Sites are hosted on our own cPanel/WHM server, which runs 200+ client sites. See managed web hosting and cloud storage and backup.
When a rebuild beats a cleanup
Cleaning is the right call for most sites. Sometimes it isn't, and we'll tell you. A rebuild is worth weighing when:
- there is no clean backup and the theme has been customised so heavily that nobody can separate original code from injected code;
- the site relies on a theme or plugin that is no longer maintained, so the hole can't be patched;
- it has been cleaned before and the infection keeps coming back;
- a redesign was already planned.
A rebuild keeps your content and is planned so the URLs Google already knows keep working. See website redesign and migration. A technical SEO check afterwards confirms Google sees the clean site.
How we handle a cleanup
Send us the site address and what you've noticed through the contact page, or call 07 3067 8910, Monday to Friday 8:30am to 5:30pm. We take a first look, tell you whether cleaning or rebuilding makes more sense, and quote before anything starts. Our in-house team is based in Pallara, Brisbane, and the work is done remotely, so the site can be hosted anywhere in Australia.
If your site is down with an error message but there's no sign of an attacker, that's a different problem. See WordPress critical error repair.
Hack symptoms and what to do about each
| What you see | What it means | How to fix it | How long it takes |
|---|---|---|---|
| Visitors from Google land on a pharmacy, casino or scam page | Injected code redirects search traffic only, so it hides from you | Full cleanup: core, plugins, .htaccess, database and cron jobs | Depends on how far it spread |
site: search shows Japanese or product spam pages | Spam pages or URL injection | Remove them, leave the URLs returning 404 or 410, resubmit the sitemap | Google drops them as it recrawls |
| "This site may be hacked" under your listing, or a red Chrome warning | Google has flagged the site | Clean the site, then Request review in the Search Console Security issues report | Google says reviews take a few days to a few weeks |
| Google Ads disapproved for "Compromised site" | Ads policy blocks hacked destinations | Pause the ads, clean the site, then appeal the disapproval | After the review clears |
| Host suspension for malware or spam | Your account is sending spam or serving malware | Clean the whole account, then ask the host to lift the suspension | Depends on the host |
Stop visitors reaching the hacked site
If customers are being sent to scam pages, stop that before you clean. Ask your host to put up a holding page or restrict the site while you work. On WordPress, a maintenance mode plugin is not enough on its own, because injected redirects can run before WordPress loads. Take your copy of the site first, so the evidence is kept.
If you run Google Ads
Google's ads policy on compromised sites covers destinations that have been hijacked or hacked. Pause any ads pointing at the site so you aren't paying for clicks that land on spam. Once the site is clean, open the disapproved ads, click Appeal on the status and say you made changes to comply. Google's help suggests giving it time to recrawl the site first. Our guide to disapproved ads and destination errors covers the appeal in detail.
Shopify, Wix and other hosted platforms
On hosted platforms the provider looks after the server, so a "hack" usually means someone got into your account. Reset your password, turn on two-step login, remove staff accounts and apps you don't recognise, check any custom code added to the theme, and contact the platform's support.
Reporting it in Australia
- Cybercrime: report it through ReportCyber at cyber.gov.au. The Australian Cyber Security Hotline is 1300 CYBER1 (1300 292 371).
- Customer data: if the site held personal information, the Notifiable Data Breaches scheme may apply. It covers businesses with annual turnover over $3 million and some smaller ones, such as health service providers. If a breach is likely to cause serious harm, you must notify affected people and the OAIC promptly.
This is general information, not legal advice.
Related problems
If the browser warning says "Not secure" rather than "dangerous", it is usually a certificate problem. See website not secure. A broken site with no attacker involved is covered in WordPress critical error repair.
When to get help
If the hack comes back, a specialist reads the server logs for the entry point, checks every site in the hosting account and hardens the server. Talk to us about secure hosting.
About this guide
Written by Amann Jhamb, Director of AR Digital Solutions, 17 years in web design, SEO and paid ads. Last checked: 3 November 2026 against Search Console Help: Security issues report. Change note: updated 3 November 2026 with a symptom table, Google Ads, hosted platform and Australian reporting sections, and new FAQs. Part of our website help centre.